Preemptive resilience platform
Preemptive resilience for APIs, agents, and critical ecosystems.
R/Pulse anticipates high and critical risks in APIs, integrations, and AI agents, before they turn into exploits or incidents.
Start with a one-time assessment. Then run it continuously or self-hosted.
The future of security is preemptive. Your APIs should be too.
The market is moving beyond purely reactive security postures. Preemptive capabilities, not just detection and response, are the future of cybersecurity.
From detecting to anticipating
Preemptive capabilities are gaining ground because organizations need to act before threats materialize.
APIs as a critical surface
APIs make up the majority of today's dynamic internet traffic. API attacks are a major concern for security leaders.
Resilience by design
Resilience needs to be built into architecture. Modern practices like 'Resilience by design' and 'AI-enabled risk sensing' modernize operational resilience programs.
In the agentic era, APIs become surfaces for action.
Agents now use tools, connectors and systems to act. When critical APIs behave unexpectedly, the impact can go beyond technical and reach security, operations, compliance and business.
Specialized modules for different risk surfaces.
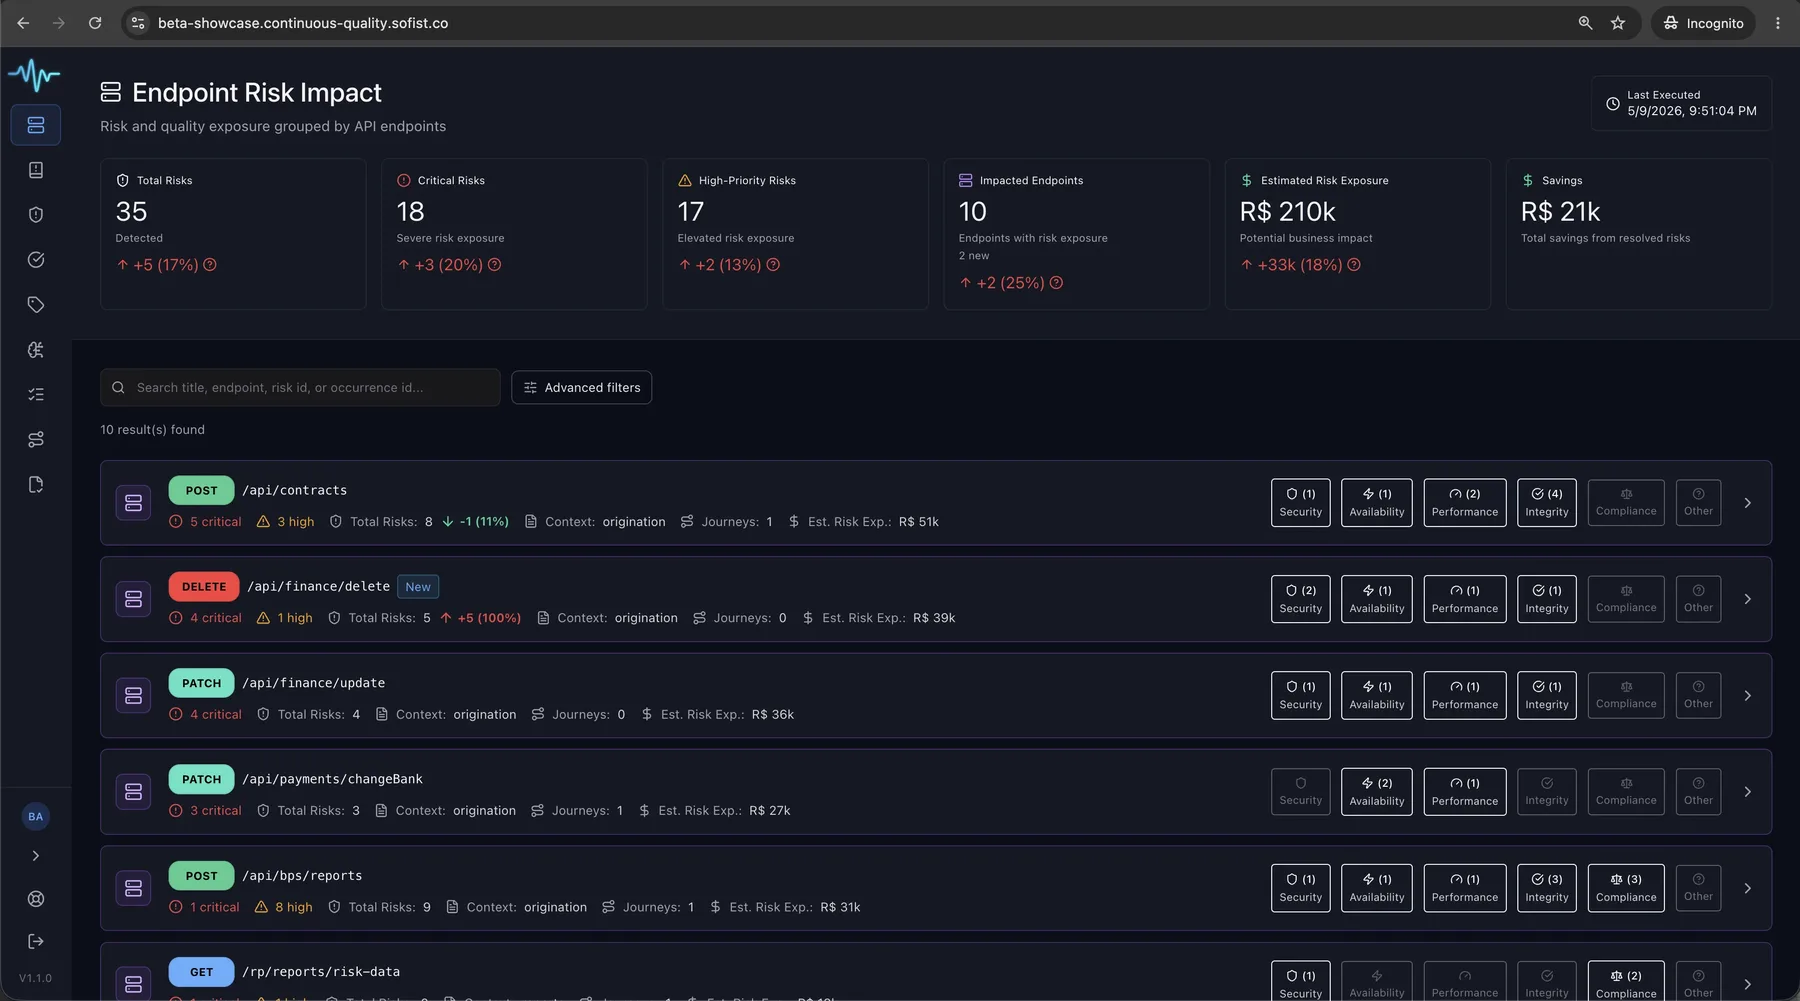
APIs, applications, and AI agents change all the time. Each R/Pulse module investigates one of these surfaces and points to what needs attention before an incident.
Continuous API validation
API Resilience Core (ARC)
Tracks changes in your APIs and points validations at what changed. Each risk comes with reproducible evidence, and a new evaluation checks the fix.
Best when
- your APIs change with every release
- a failure hits customers, transactions, or partners
- manual revalidation eats up the team's time
Continuous Pentesting
Autonomous Adaptive Security Agent (AASA)
A Continuous Pentesting agent that expands your security team's capacity. It investigates application changes without waiting for the next pentest, within the scope you define.
Best when
- the application changes between pentests
- the security team can't assess as often as needed
- fixes need a retest
Active validation of AI agents
Agent Resilience & Observability (ARO)
Simulates situations off the expected path to see how your AI agents respond and act. Shows what to review before expanding each agent's autonomy.
Best when
- your agents access data, tools, or systems
- you plan to expand an agent's autonomy
- several teams are adopting AI agents



See how R/Pulse helps your role.
Security, engineering, governance, architecture, and AI leaders see different risks. R/Pulse translates API resilience into the decision each team needs to make.
Start point-in-time. Evolve when it makes sense.
R/Pulse can start with a point-in-time execution on critical surfaces, evolve to continuous CI/CD operation, or be deployed in a self-hosted model when governance, security, or regulation require more control.
Point-in-time execution
Assess critical endpoints, journeys, or integrations, discover high and critical risks, and generate evidence to guide decisions, prioritization, and action plans.
Continuous operation
Incorporate preemptive resilience into the development cycle to track changes, re-evaluate fixes, and reduce dependency on manual analyses.
Self-hosted / Enterprise
Operate in an environment controlled by the organization, with its own infrastructure and greater adherence to internal security, data, and AI policies.
In the API Resilience Core module, if no high or critical risks are found within the agreed scope, you do not pay for the point-in-time execution.
See security, governance and deployment features
| ISO 27001:2022 | Certified |
| SSO | Available |
| Role-based access control | Available |
| Audit logs | Available |
| Encryption at rest and in transit | Always on |
| Self-hosted deployment | Available |